ISO 27001 IMPLEMENTATION TOOLKIT
Build Your ISO 27001 ISMS Without Starting From Scratch.
Building an ISMS requires more than understanding the standard. You need policies, risk documentation, registers, procedures, audit materials, management-system documentation, and a practical way to bring everything together.
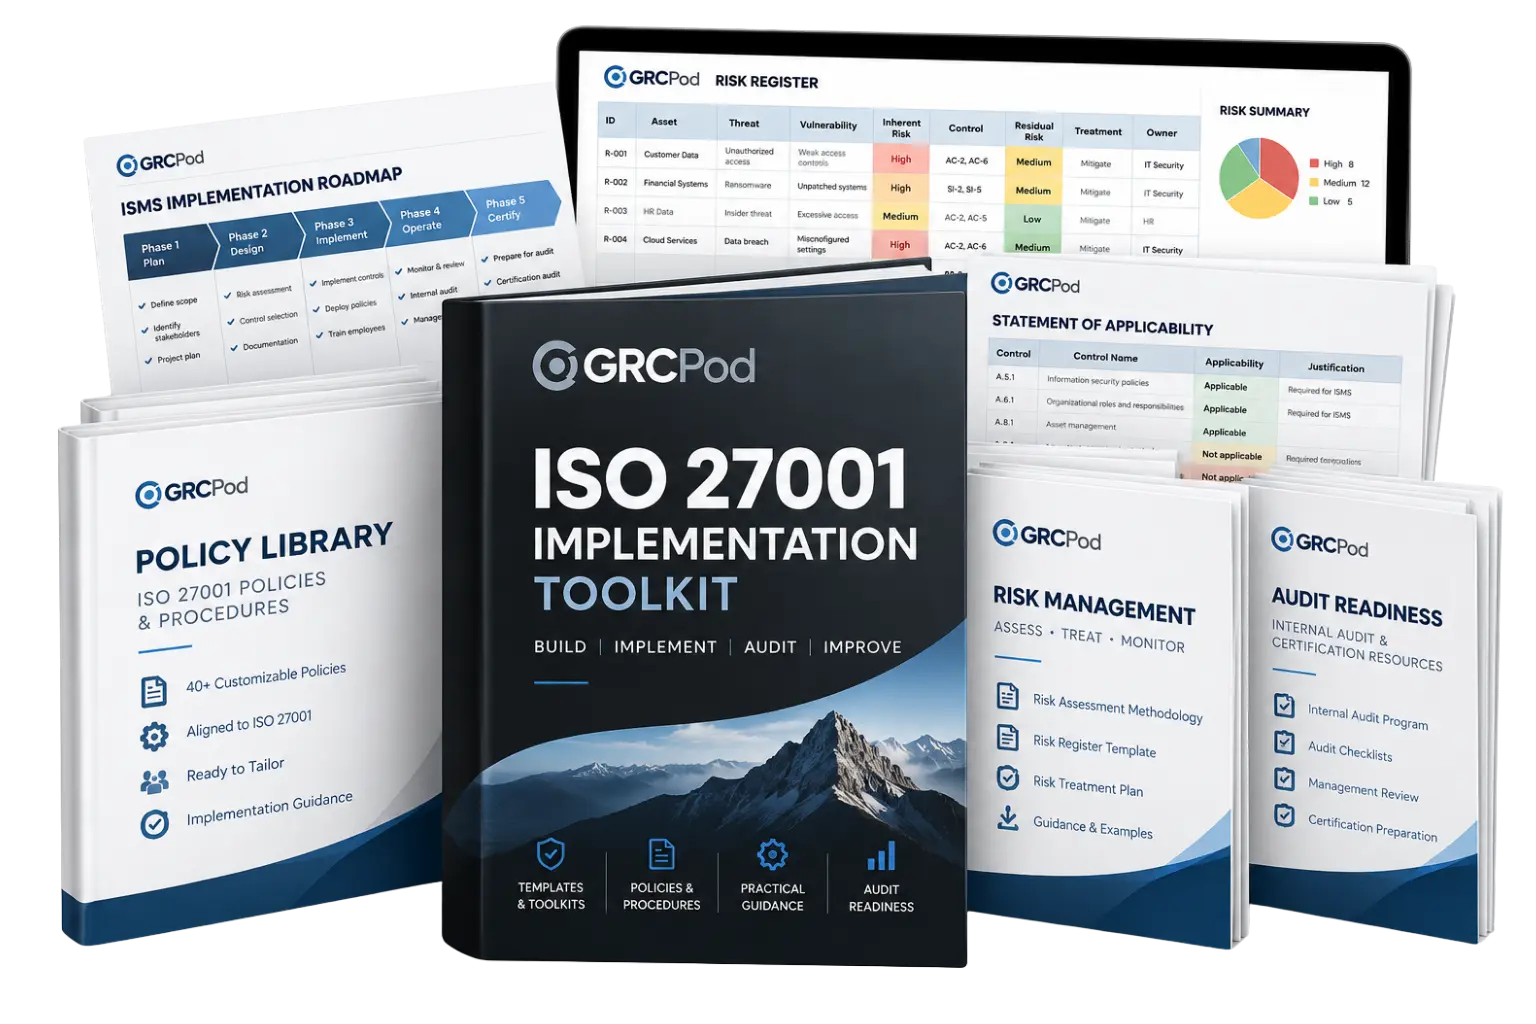
The GRCPod ISO 27001 Implementation Toolkit gives you a structured starting point for building and operating your ISMS, with editable documents, spreadsheets, policies, registers, SOPs, and implementation resources you can adapt to your organization.
$499 · One-Time Purchase
FROM STANDARD TO WORKING ISMS
Knowing What ISO 27001 Requires Is
Only the Beginning.
You can read the standard. You can study Annex A. You can understand the certification process.
Then comes the harder part:
Turning those requirements into an information security management system your organization can actually operate.
That means defining scope. Establishing responsibilities. Creating a risk methodology. Performing risk assessments. Determining necessary controls. Building your Statement of Applicability. Establishing policies and procedures. Defining objectives. Maintaining records. Conducting internal audits. Holding management reviews. Managing corrective actions.
And making sure all of those pieces work together.
If you build everything yourself, you're not just implementing ISO 27001.
You're also deciding how every document should be structured, what each register should contain, how the pieces should relate, and what needs to exist before you can move to the next stage.
That's the work the toolkit is designed to accelerate.
The GRCPod ISO 27001 Implementation Toolkit gives you the underlying documentation structure so you can spend less time staring at blank documents and more time adapting the ISMS to how your organization actually operates.
A PRACTICAL IMPLEMENTATION SYSTEM
Start With the Structure. Make the ISMS Your Own.
The toolkit is not a collection of finished documents that you simply rename and submit to an auditor.
It gives you something more useful:
A structured starting system for building your own ISMS.
The documents are editable so you can adapt them to your organization's scope, risks, technologies, responsibilities, processes, regulatory obligations, contractual requirements, and actual operating practices.
Instead of deciding how to construct every policy, register, methodology, plan, procedure, and record from the ground up, you begin with a practical foundation and focus your effort where it belongs: making the ISMS accurately reflect your organization.
INSIDE THE TOOLKIT
The Documentation Infrastructure for
Building Your ISMS
Practical templates, tools, and implementation resources to help you structure, build, and manage your ISO 27001 ISMS.
Core ISMS Documentation
Build the management-system foundation required to structure, govern, evaluate, and improve your ISMS.
Includes resources for:
Risk & Control Management
Move from general security concerns to documented, structured risk and control decisions.
Includes:
These resources provide a starting structure for documenting how your organization identifies, analyzes, evaluates, treats, and tracks information security risk.
Information Security Policy Library
Start with an extensive editable policy foundation covering common information security and ISO 27001 implementation areas.
Policies Include:
Every organization is different. Use the policies that apply, modify them to reflect your actual environment, and remove what doesn't belong.
Supporting ISMS Documentation
Support the broader operational environment around the management system.
Includes:
ISMS Records & Registers
Policies describe what should happen.
Your ISMS also needs records that help demonstrate and manage what actually happens.
The toolkit includes editable registers and logs for:
These provide practical starting structures for maintaining important ISMS records over time.
Standard Operating Procedures
Move from policy statements into repeatable operational processes.
Included SOPs cover:
The SOPs are editable so responsibilities, systems, approval paths, and operating steps can be adapted to your environment.
MORE THAN A POLICY PACK
Bring the Pieces Together Into an Implementation Plan.
A folder full of policies isn't an ISMS.
That's why the toolkit also includes resources designed to help organize the implementation itself.
ISMS Implementation Plan
A structured implementation resource to help organize the work required to establish your ISMS.
Document Library
A central reference for understanding and organizing the documentation included in the toolkit.
ReadMe First
Guidance for navigating the toolkit and understanding how the resources are organized.
Together, these resources help you approach the toolkit as an implementation system rather than a random collection of files.
FROM TOOLKIT TO YOUR ISMS
Use the Toolkit as a Starting Point, Not a Shortcut Around the Work.
Define your ISMS scope, organizational context, responsibilities, implementation priorities, and applicable requirements.
Adapt the relevant policies, methodologies, registers, plans, procedures, and supporting documentation to your organization.
Assign ownership, perform your risk assessment, implement necessary controls, maintain records, measure performance, and operate the processes you've documented.
Use internal audit, management review, corrective action, monitoring, and continual improvement to evaluate whether the ISMS is operating as intended.
BUILT FOR IMPLEMENTATION
The Value Isn't Having More Documents. It's Not Having to Invent Every Document Yourself.
You could build an ISO 27001 ISMS from scratch.
For some organizations, that may be the right approach.
But consider the work involved before implementation even begins:
Determining the structure of your risk register. Building risk evaluation criteria. Designing the Statement of Applicability. Structuring an internal audit program. Creating audit reports and schedules. Developing management review documentation. Building policy frameworks. Creating operational registers. Establishing corrective action records. Developing SOPs.
None of that eliminates the need for professional judgment.
But neither does all of it need to begin with a blank Microsoft Word or Excel file.
The GRCPod toolkit gives you a developed starting point so your time can go toward making the ISMS appropriate for your organization rather than reinventing its basic documentation infrastructure.
IS THIS TOOLKIT FOR YOU?
Built for the People Responsible for
Making ISO 27001 Work.
The toolkit is designed for:
It may not be right for you if:
BUILT TO BE CUSTOMIZED
Your ISMS Should Describe Your Organization. Not Ours.
The toolkit is provided in familiar editable Microsoft Office formats, including Word, Excel, and PowerPoint.
That means you can adapt:
The goal isn't to make your organization look like the toolkit.
The goal is to use the toolkit to accelerate the creation of an ISMS that looks like your organization.
GET THE COMPLETE TOOLKIT
ISO 27001 Implementation Toolkit
A practical, editable starting system for building and operating your ISO 27001 ISMS.
Your toolkit includes:
$499
Instant digital access after purchase.
One-Time Purchase. No subscription.
Frequently Asked Questions
Is this an ISO 27001 certification package?
No. The toolkit provides editable documentation, tools, and implementation resources to help you build and operate an ISMS. Purchasing or completing the toolkit does not certify your organization or guarantee that it will achieve ISO 27001 certification.
Are the documents ready to use as-is?
They are designed to be customized.
Your organization has its own scope, risks, technologies, responsibilities, legal and contractual requirements, processes, and control environment. The documentation should be reviewed and adapted accordingly.
What file formats are included?
The toolkit uses editable Microsoft Office formats, primarily Word and Excel, with PowerPoint resources where applicable.
Does the toolkit include a Statement of Applicability?
Yes. The toolkit includes an editable Statement of Applicability resource along with risk assessment and control-management resources that support the broader risk treatment process.
Does it include an information security risk register?
Yes. An editable Information Security Risk Register is included, along with risk assessment methodology, analysis and evaluation criteria, a questionnaire, a report template, and a risks and threats catalog.
Does it include internal audit resources?
Yes. The toolkit includes an Internal Audit Program Overview, Internal Audit Checklist, Internal Audit Report Template, and Internal Audit Schedule.
Does it include policies?
Yes. The toolkit contains an extensive information security policy library covering more than 30 common areas, including access control, asset management, backup, encryption, incident management, logging and monitoring, network security, physical security, remote working, third-party risk management, vulnerability management, data protection, and others.
Do I need to use every document and policy?
No.
Your documentation should be appropriate to your organization and ISMS. The toolkit provides a broad implementation foundation. Determine which resources apply, customize them, and avoid maintaining documents or processes simply because a template exists.
Will this guarantee that we pass an ISO 27001 audit?
No.
Certification depends on your organization's implementation, operation of the ISMS, evidence, applicable requirements, audit results, certification body, and other factors. No legitimate documentation toolkit can guarantee certification.
Is this legal or certification advice?
No. GRCPod provides informational, educational, and operational resources. The toolkit does not constitute legal, regulatory, certification, audit, or other professional advice specific to your organization.
Can consultants use the toolkit for clients?
The standard license should govern permitted use. If you intend to use the toolkit across multiple unrelated client organizations, contact GRCPod regarding appropriate licensing.
Don't Start Your ISMS With a Blank Page.
Start with the documentation, tools, policies, registers, procedures, and implementation structure already built.
Then make them yours.
$499 · One-Time Purchase
© Copyright GRCPod.com. All Rights Reserved
GRCPod provides general informational and educational content about governance, risk, compliance, information security, and related topics. Content on this site does not constitute legal, regulatory, certification, audit, or professional advice. Requirements and circumstances vary by organization, jurisdiction, framework, and certification body. Always evaluate applicable requirements and obtain qualified professional guidance when appropriate.