ISO implementation, clauses, Annex A, certification, SoA, audits, ISMS
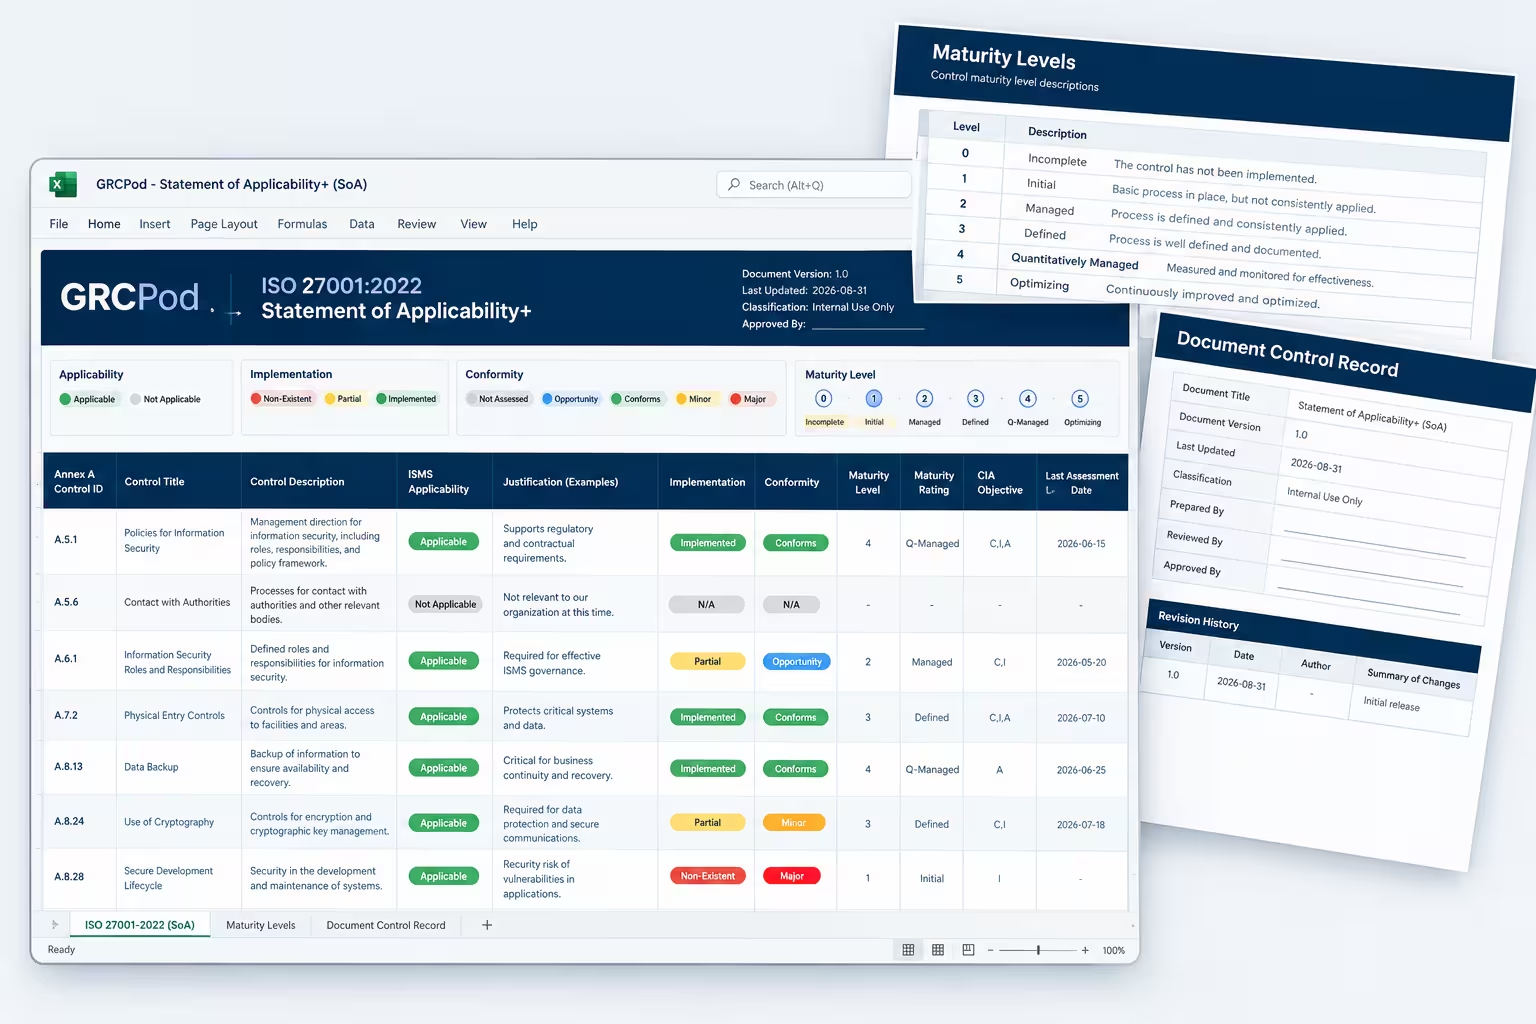
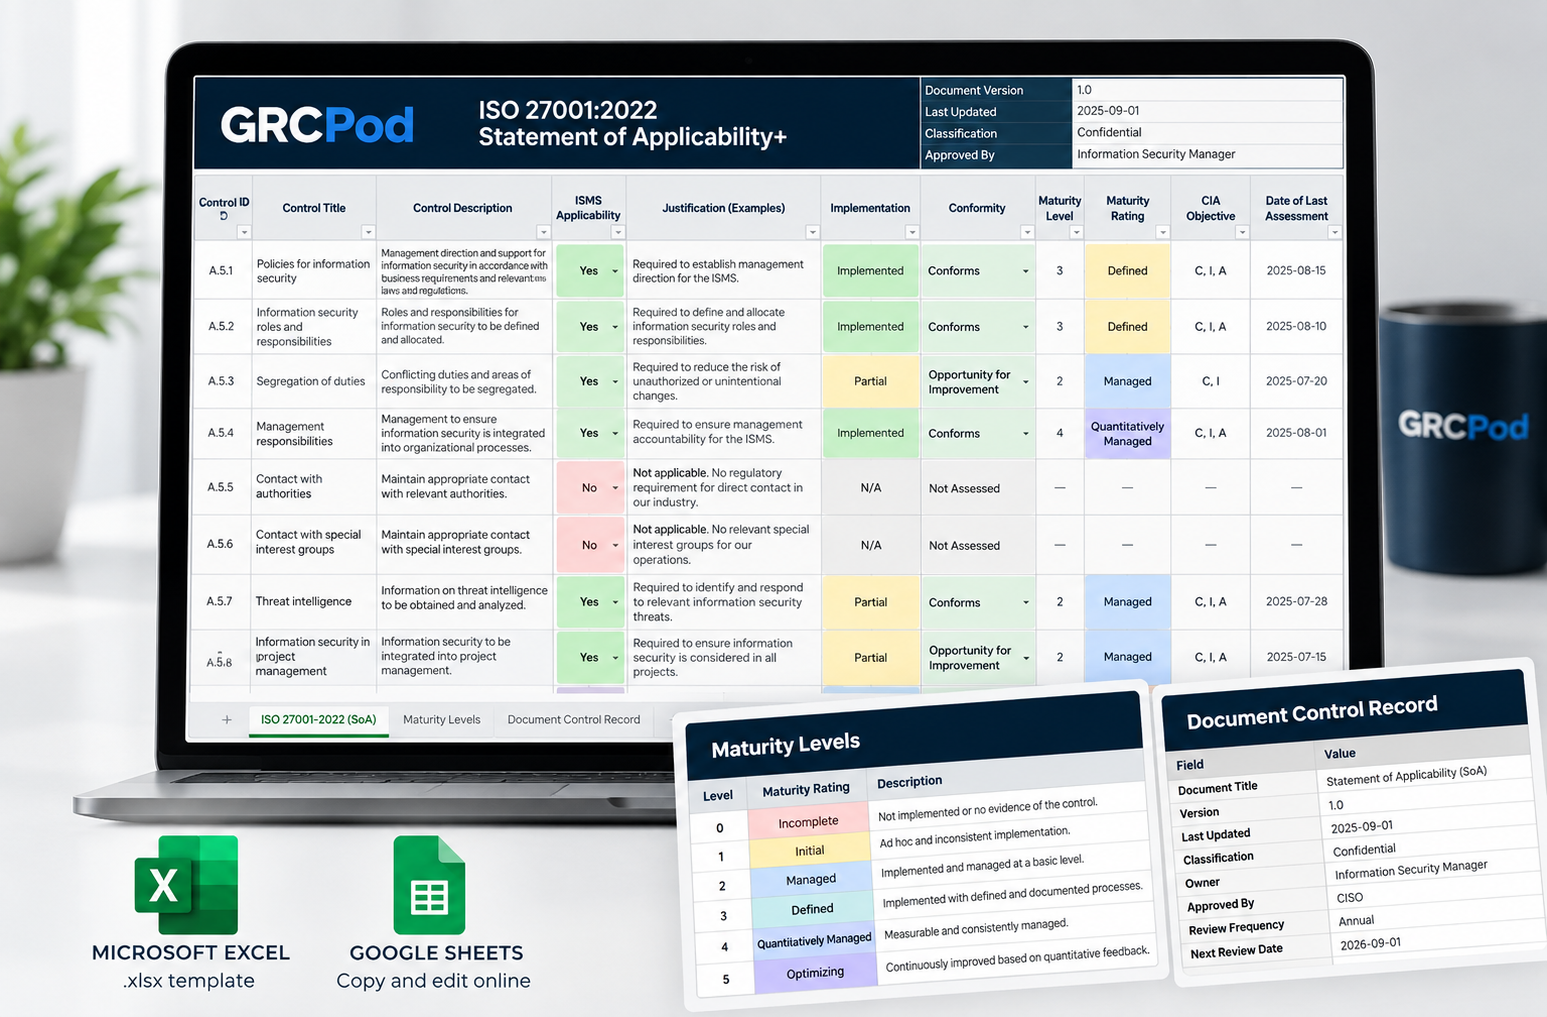
Get our free ISO 27001:2022 Statement of Applicability+ template, complete with all 93 Annex A controls, example justifications, and optional control assessment features.
Available in Microsoft Excel and Google Sheets. Enter your email below, and we'll send you the download guide with links to both versions.
We'll use your email to deliver your free template.
No. SPAM. You can unsubscribe at any time.
About | Contact | LinkedIN | Editorial Policy
© GRCPod.com. All Rights Reserved
GRCPod provides general informational and educational content about governance, risk, compliance, information security, and related topics. Content on this site does not constitute legal, regulatory, certification, audit, or professional advice. Requirements and circumstances vary by organization, jurisdiction, framework, and certification body. Always evaluate applicable requirements and obtain qualified professional guidance when appropriate.